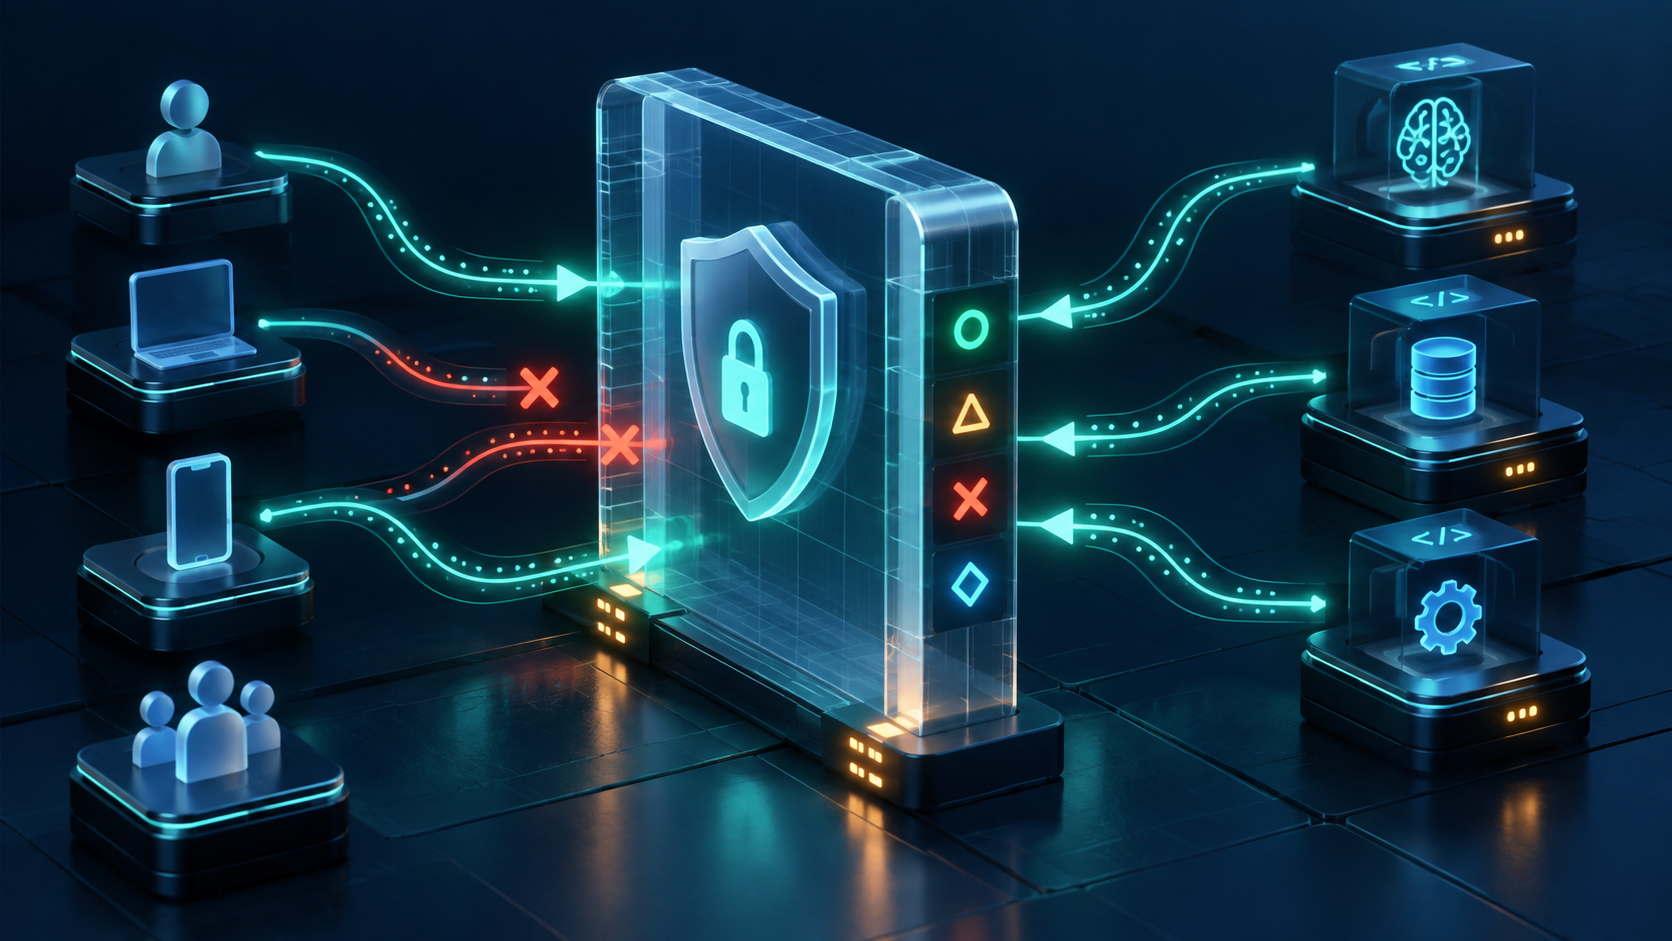
MCP servers can give AI clients access to real systems: source code, issue trackers, files, cloud services, and internal data. That capability is useful, and it makes basic access design important. A connection that is convenient for one developer may grant too much access when shared across a team.
There is no single switch that makes an MCP deployment secure. A strong baseline combines identity, least privilege, secret protection, runtime isolation, and operational visibility. Apply these controls at the client, gateway, server, and infrastructure layers that your setup uses.
1. Grant the smallest useful access
Begin by listing the people and applications that need each server. Give access to the specific users or roles that need it, and review that access when responsibilities change. Avoid making every installed server available to every user by default.
Where tools support different actions, separate read-only tasks from actions that modify or delete data. Use approval steps for higher-impact operations where the workflow allows it. These controls should be enforced by the server or gateway rather than relying only on an AI prompt to avoid an action.
2. Treat credentials as secrets
API keys and OAuth tokens should not be copied into public repositories, shared chat messages, or configuration files that are broadly readable. Prefer a managed secret store or a gateway designed to protect and apply credentials. Limit each credential to the permissions the connected server requires, and rotate or revoke it when it is no longer needed.
Check where credentials travel: from the administrator who configures them, through the gateway, and to the server. Understand which components can read a secret and what happens to it in backups and logs.
3. Isolate server processes
For servers you run yourself, consider what files, network destinations, environment variables, and host resources the process can access. Containerization can provide useful boundaries, but the actual protection depends on configuration: mounted paths, privileges, networking, and resource limits all matter.
Keep the gateway and server runtimes updated, and avoid running tools with broader host access than their function needs. Treat third-party server packages as software dependencies: review the source and publisher, pin versions where practical, and understand the permissions they receive.
4. Make activity reviewable
Logs help answer operational questions: which user made a request, which server handled it, when it happened, and whether it succeeded. Decide what detail is appropriate to retain, who can view it, and how long it should be kept. Avoid logging secret values or sensitive payloads unless there is a clear reason and suitable protections.
Test that audit events are actually generated for the paths you care about. A dashboard showing server status is useful, but it is not the same as a request audit trail.
5. Protect the deployment itself
Restrict access to the gateway’s administration interface. For public deployments, use HTTPS and a firewall or reverse proxy configured for the connection patterns your clients require. Back up persistent data and keys together where the application depends on both to restore credentials or records.
Put the controls in one place
For teams managing multiple clients and servers, a gateway can provide a central point for authentication, policies, credential management, and activity records. It does not replace server-level permissions or infrastructure security; it helps apply shared controls consistently across connections.
MCPlama is an open-source, self-hosted MCP gateway with user and role access policies, credential management, and activity tracking. Review the documentation to understand its deployment and security model.
Keep learning
Plan the deployment and day-two operations for your MCP environment.
Read the self-hosting guide →